 Fiber Optic ataupun dalam bmnye dikenali dgn nama gentian optikdigunakan sebagai perantaraan (medium) bagi telekomunikasi dan jaringan komputer kerana ianya sangat mudah lentur dan boleh diikat sebagai kabel. Walaupun gentian boleh diperbuat daripada plastik lutsinar atau kaca, gentian yang digunakan dalam telekomunikasi jarak jauh hampir selalunya menggunakan kaca, kerana penyerapan optik yang lebih rendah
Notes -> Fiber Optic
7:20 PM | 0 Comments
Fiber Optic ataupun dalam bmnye dikenali dgn nama gentian optikdigunakan sebagai perantaraan (medium) bagi telekomunikasi dan jaringan komputer kerana ianya sangat mudah lentur dan boleh diikat sebagai kabel. Walaupun gentian boleh diperbuat daripada plastik lutsinar atau kaca, gentian yang digunakan dalam telekomunikasi jarak jauh hampir selalunya menggunakan kaca, kerana penyerapan optik yang lebih rendah
my netsec pro silibus
11:56 PM | 0 Comments
- Objectives Security Teory
- 3 Step Chipping
- Ip Addressing
- Subnetting
- Network Cabling
- Cisco Router
- Fiber Optic
- Linux Router
- Sniffer
- SQL Injection
- Mod Security
- XSS Remote
- SQL Injection
- Remote File Inclusion
- Window Firewall
- Web Server
- Samba
- Linux Firewall
Notes --> Virus Micro Generator
9:09 PM | 0 Comments
Tools – Macro – Visual Basic Editor - This DocumentTulis :
Sub FileSaveAs() ----------------check at Tools – Macro – Macro – choose word commandMsgBox “Padan Muka”
End Sub
To Protect :Tools – Macro – Security – choose very high
Notes --> Mod Security
8:55 PM | 0 Comments
Notes -> Setting Samba
12:10 AM | 0 Comments
* untuk security(kalo folder ada dalam linux)
1. rpm -q samba
*nak check ada samba @x
*install samba (cd,internet,server)
2. yum -y install samba
*download & install trus dari internet
*/sbin/ifconfic -> nak check ip pc
*wget http://10.1.0.11/fedora/pacakges/samba -3.0.26a-6.fc8.1386.rpm
3.edit samba configuration
*security=user
*workgroup=_____
4.create share folder [xyz]
*path=/xyz ->folder mana
*writeable=yes ->bole save/write
*browse dble=yes ->org bole browse
5.create folder to share
*ex:/xyz
* #mkdir /xyz
* #chmod 777/xyz
6.create Linux user account & samba account
* add user insep
* password insep
* smb password -a insep
notes -> Try Linux Command
12:06 AM | 0 Comments
Notes -> Web Server
11:57 PM | 0 Comments
*more on remote control computer
*bole control server dr jarak jauh
FTP
*file transfer protocol
*tranfer file
*bole ftp ke pc org lain/hos/server
Web
*jadikan web sebagai server dari jarak jauh
*kena install apachee
---->> dalam linux kena "up"kan dulu dengan menggunakan command
/sbin/service sshd start - ssh
/sbin/service ftpd start - ftp
/sbin/service httpd start - web
---->> check status
*run
*stop
Notes -> Cont- Linux Router
11:49 PM | 0 Comments
- linux save budjet sebab most of the application in linux are free
- not less 2% virus only will effect linux
- open source code
- acting as server and can acting as client
- linux is stabil than microsoft
- linux is sesuai as a server
Notes -> Linux Router
11:27 PM | 0 Comments
- at least 2 network card
- 2 cross cable
- install fedora 8 (for configuration)
2. What u need to do?
- set IP forwarding
- set IP
- routing (buat routing + gw)
* Linux router guna command line untuk configuration
1. nak upkan network card
service network restart
/etc/init.d/network restart
eth0 .................................[/]
eth1 ................................ [/]
2. set ip
/sbin/ifconfig eth0 192.168.1.1 netmask 255.255.255.0 broadcast 192.168.1.255
3. set gateway
/sbin/route add-net 192.168.1.0 netmask 255.255.255.0 gw 192.168.1.255 dev eth0
4. set ip_forwarding
echo 1 > proc/sys/net/ipv4/ip_forward
(0 untuk stop) dan (1 untuk up)
5. tengok routing table
/sbin/ip route show
6. tengok ada routing @ x
/sbin/route -v
7. delete routing dalam routing table
/sbin/route del -net ............./sm
8. up network card one by one
/sbin/if up eth0
/sbin/if up eth1
** if pc <-> x bole nak ping:
- firewall pc x off
- anti virus x off
- ip_forwarding tiap kali x up
- firewall linux->ip table
6.
Notes -> Window for Firewall
6:07 PM | 0 Comments
1.What is firewall
firewall control in/out bound(communication) network traffic
2.how its work?
it just have 2 activities. there are allow and deny
3.is it anti virus ? -not an anti virus
it is not an anti virus. it just have a rules that are controlling traffic that are allow or deny any network from other
firewall control in/out bound(communication) network traffic
2.how its work?
it just have 2 activities. there are allow and deny
3.is it anti virus ? -not an anti virus
it is not an anti virus. it just have a rules that are controlling traffic that are allow or deny any network from other
 4.What is proxy server proxy server bole jugak dikatakan sebagai orang tengah
5.What is application that can allow you to access any website
These site will allow you to access any block website. There are:
http://www.proxyblind.org/
http://www.kortaz.com/
http://www.a-bypass.com/
http://www.yourprox.com/
http://www.myspaceproxy1.com/
http://www.topproxy.com/
http://www.vtunnel.com/
http://www.offsurf.com/
http://www.antibloxx.com/
http://www.43proxies.com/
http://www.s67.net
proxy sometimes can be:
- firewall
- filtering
- gateway

Apabila terima respon, proxy akan copy content yang diminta oleh client pada dirinya sendiri dan satu keadaan lagi ianya akan hantar content tersebut kepada clientnya.
Notes -> Remote File Inclusion
11:21 PM | 0 Comments
remote computer.
Notes -> Remote SQL Injection
5:20 PM | 0 Comments
*Salau sql injection, ianya akan berlaku pada menu login untuk kita dapatkan username dan password
Remote SQL Injection
Ianya berlaku pada bahagian url @ address di mana kita akan "paste"kan injection pada text area url utk dapatkan username dan password
dimana:
username = plaintext
passwoord = hash (r7hy89p10) ::> yg x bole difahami
utk dptkan pswrd kita kena dapatkan md5 coder @ base64 coder
Notes -> XSS @ Cross Site Script
8:03 PM | 0 Comments
example: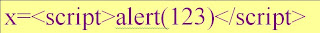
XSS berlaku pada ->
RFI berlaku pada ->
XSS berlaku pada ->
RFI berlaku pada ->
Notes -> Continue * SQL Injection
8:33 PM | 0 Comments
1. Kita gunakan if...else statement pada bahagian login
2. Escape from all single quote ('')
example:
Username : 1'or'1'='1
Password : 1'or'1'='1
$SqL="Select namapenyelia, tahap_penyelia, id_penyelia
from penyelia where username='$name' and password='$pass'
if($name="1'or'1'='1"){break;} ->mana-mana username yang ada "quote" kita reject
Tujuan if...else statement adalah untuk :
1.Check $name (variable) contain.
2.Reject kalau ada single quote.
Another way to protect your website:
1. Encrypt HTML files and hide source code
2. Disable content filters
3. Block website rippers
4. Customize HTML and add some effects
more info ->http://www.aerotags.com/products/tlp.php
Notes -> SQL Injection
12:06 AM | 0 Comments
Notes -> Maqic Quote
10:54 PM | 0 Comments
1' or '1' = '1
Happy Chinese New Year
11:59 PM | 0 Comments
Notes -> Sniffer
4:52 PM | 0 Comments
Is a program that monitors and analyzes network traffic, detecting bottlenecks and problems. Using this information, a network manager can keep traffic flowing efficiently. A sniffer can also be used legitimately or illegitimately to capture data being transmitted on a network. A network router reads every packet of data passed to it, determining whether it is intended for a destination within the router's own network or whether it should be passed further along the Internet. A router with a sniffer, however, may be able to read the data in the packet as well as the source and destination addresses. Sniffers are often used on academic networks to prevent traffic bottlenecks caused by file-sharing applications. The term "sniffer" is occasionally used for a program that analyzes data other than network traffic. For example, a database could be analyzed for certain kinds of duplication.